
I’m not leaving SEO.
I should probably start there.
Cybersecurity has become another area of technology I want to understand, but I’m not approaching it with a dramatic career-change announcement or a deadline for becoming a security professional.
I’m approaching it the same way I originally approached SEO:
I’m curious, so I’m learning.
The difference this time is that I have years of experience working with websites and technology to build from.
My starting point was the Google Cybersecurity Certificate
I needed structure.
Cybersecurity is enormous. Search for “how to learn cybersecurity” and within 20 minutes you’ll have 37 browser tabs open covering ethical hacking, networking, Linux, Python, cloud security, certifications and somebody telling you to build a home lab immediately.
I decided to start with the Google Cybersecurity Certificate.
It gave me an introduction to security fundamentals, risk management, networks, Linux, SQL, threats and vulnerabilities, incident response and Python.
More importantly, it helped me identify what I don’t know.
Now the goal is to go deeper.
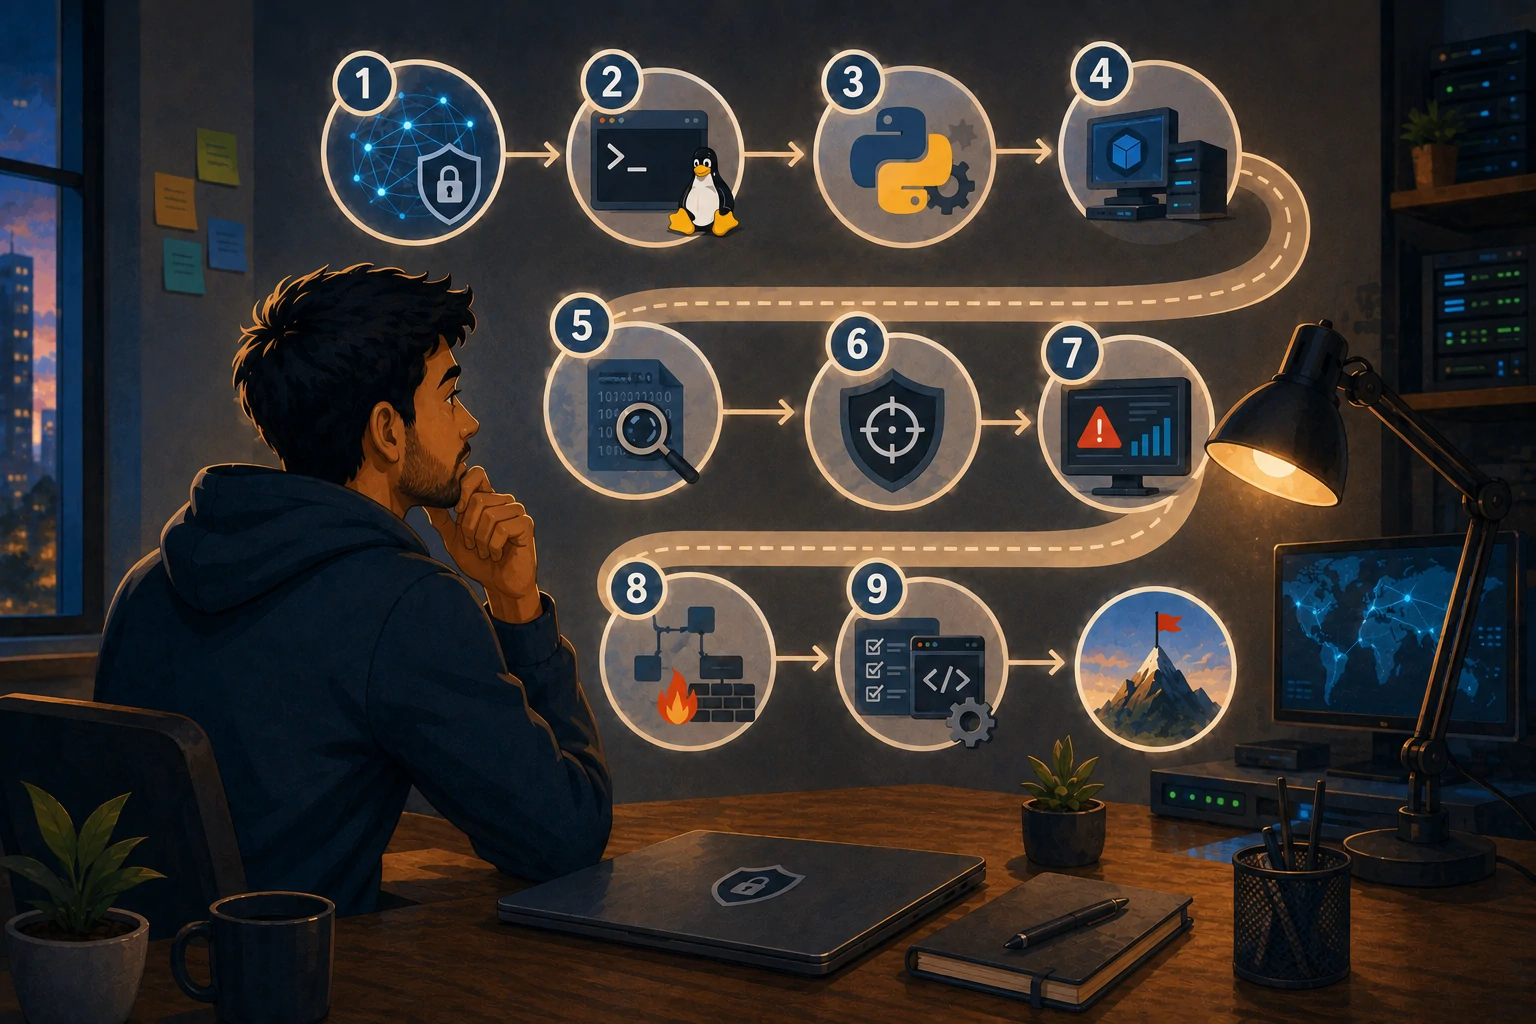
Step 1: Understand networking properly
This is probably my biggest priority.
I’ve encountered networking concepts throughout my SEO career.
DNS comes up during migrations.
HTTP status codes are part of everyday technical SEO.
CDNs affect how websites are delivered.
Servers, requests and browsers are things I’ve worked around for years.
But knowing enough about something to do SEO isn’t the same as understanding it properly.
I want to become more comfortable with concepts such as TCP/IP, ports, protocols, DNS, firewalls, routing and how devices actually communicate.
Cybersecurity makes much more sense when you understand what you’re trying to secure.
Step 2: Get comfortable with Linux
I don’t want Linux commands to be something I memorise for a course and immediately forget.
I want to use them.
That means spending more time in the terminal, navigating directories, working with files, understanding permissions, and gradually becoming comfortable without relying on a graphical interface for everything.
This is an area where I expect repetition to matter more than reading.
Use it.
Forget a command.
Look it up.
Use it again.
Eventually, it sticks.
Step 3: Keep learning Python
Python sits in an interesting position for me because it connects several things I’m interested in.
SEO.
Data.
Automation.
Cybersecurity.
I’m not trying to become a software engineer.
I want to become capable enough to look at a repetitive problem and think:
“I could probably automate this.”
For cybersecurity, that could eventually mean working with logs, processing files or analysing information.
For SEO, it could mean automating parts of audits, working with APIs or processing large datasets.
One language. Several possible uses.
That makes it worth investing in.
Step 4: Build a home lab
This is where I want the learning to become less theoretical.
Courses are useful, but there’s a limit to how much you can understand by watching somebody else do something.
I want an environment where I can experiment safely.
Virtual machines.
Linux.
Networking.
Logs.
Different operating systems.
Security tools.
The point isn’t to create some movie-style hacker setup with six monitors and green text everywhere.
It’s to have somewhere I can break things without breaking anything that matters.
I learn much faster when I have to figure out why something isn’t working.
Step 5: Practise investigating things
Incident detection and response was one of the areas of cybersecurity that caught my attention.
Maybe that’s because it reminds me slightly of the investigative side of SEO.
Something changes.
You don’t immediately know why.
You gather evidence.
You look through data.
You identify patterns.
You form a theory.
Then you try to prove yourself wrong.
Obviously, investigating a security incident is very different from diagnosing an organic traffic drop.
But I enjoy that way of thinking.
I want to spend more time working with logs, alerts and realistic security scenarios where I have to understand what happened rather than simply memorise the definition of an attack.
Step 6: Learn by doing
This is where platforms with practical cybersecurity labs become interesting to me.
I want to move from:
“I know what this term means.”
to:
“I’ve actually used this.”
There’s a huge difference.
My plan is to gradually work through hands-on exercises involving networking, Linux, security fundamentals, investigation and defensive security.
I’m deliberately not trying to jump straight into the most advanced material.
Foundations first.
Step 7: Understand the defensive side of security
When people think about cybersecurity, hacking gets most of the attention.
I find the defensive side increasingly interesting.
How do you know something suspicious is happening?
What information gets recorded?
How do security teams investigate alerts?
How do you distinguish unusual behaviour from malicious behaviour?
What happens after an incident is detected?
I’m particularly interested in learning more about security operations and incident response.
That may change as I gain more exposure to the field.
I’m okay with that.
This is a roadmap, not a contract.
Step 8: Find the connections with SEO
I’m not learning cybersecurity in isolation from the career I’ve already built.
I want to understand where the disciplines overlap.
Website compromises and search spam are an obvious example.
But there are others.
Server logs.
DNS.
HTTPS.
Security headers.
JavaScript.
Access and permissions.
Website migrations.
Bots.
Infrastructure.
I’ve encountered several of these things from the search side.
Now I want to understand what they look like from the security side.
That doesn’t make cybersecurity another branch of SEO.
It makes me better informed when the two worlds meet.
Step 9: Build small projects
Eventually, I want something to show for the learning beyond certificates.
Not necessarily huge projects.
Small ones are fine.
A Python script that analyses a log file.
A documented home-lab setup.
A network analysis exercise.
An incident investigation.
Something useful that combines Python with SEO or security.
And I’ll probably write about the failures too.
Those may be more useful than the projects that work immediately.
I’m deliberately not putting an end date on this
I could turn this into one of those:
“Become a cybersecurity professional in six months” roadmaps.
But that isn’t really what I’m doing.
I already have a career I’m invested in.
This is about expanding what I understand.
Maybe cybersecurity eventually becomes a bigger part of my professional life.
Maybe I find a particular area of security that completely changes my direction.
Or maybe the knowledge simply makes me a more technically capable SEO professional.
I don’t need to know the outcome yet.
From search to security
My career in SEO started because I wanted to understand what happened after a website went live.
Now my curiosity is moving further down the stack.
How did that request reach the server?
What’s happening across the network?
Who has access?
What gets logged?
What happens when someone tries to exploit it?
How would we know?
Those questions have opened another rabbit hole.
For now, my roadmap is simple:
Learn the fundamentals. Practise them. Build things. Break things safely. Document what I learn. Keep going.
That’s how I learned much of what I know about SEO.
I’m curious to see where the same approach takes me with cybersecurity.
